A security data lake is a central repository that lets you store, manage, and analyze large volumes of security data long-term. It supports threat hunting, investigations, and analysis across security tools without the retention limits and ingest costs of traditional platforms.
A data lake stores raw data in its native format, free from predefined structures. A security data lake applies that model specifically to security telemetry: firewall logs, intrusion detection events, endpoint data, identity events, cloud audit trails, and more.
Why are security data lakes on the rise?
Traditional tools cannot keep up. Modern IT environments generate more diverse security data than legacy platforms were designed to handle. According to IDC's Worldwide SIEM Forecast (2025), the SIEM market continues to grow at a double-digit rate, but ingest-based pricing means the more visibility you pursue, the more you pay. That creates a perverse incentive: log less, or blow the budget.
Independent research shows the impact. The SANS 2025 SOC Survey found that 42% of SOCs dump all incoming data into a SIEM without a retrieval or management plan, increasing both noise and cost. Threat hunters report that lack of access to historical data hampers investigations.
Security data lakes address that gap. They provide a central, scalable repository for full-fidelity telemetry, enabling better threat detection, faster response times, and a more proactive security stance. As enterprises adopt zero trust models and expand their digital footprint, security data lakes are used for cyber defense.
Security data lake vs SIEM: what's the difference?
Both a security data lake and a security information and event management (SIEM) solution are part of an overall security strategy. They have different roles and work together.
A common approach is to tier data: send high-value, detection-critical data to the SIEM and route everything else to the security data lake, where it stays searchable for investigations, audits, and analytics. Organizations that adopt this model report faster searches and lower costs. A global hospitality leader working with Deloitte and Cribl achieved searches up to 20x faster in their data lake than in their legacy SIEM, while reducing costs and increasing total retention (Cribl and Deloitte case study, 2026).
What are the best practices for implementing a security data lake?
Set yourself up for success by following these five steps:
Define clear objectives. Identify the data you need to collect, the threats you want to detect, and the compliance requirements you must meet before you build anything.
Integrate and centralize. Make sure your security data lake ingests data from every relevant source: network logs, application logs, endpoint data, threat intelligence feeds, and cloud services.
Tier your data. Categorize data by access frequency and importance. Hot data feeds real-time detection; warm and cold data stays affordable but searchable.
Lock down access. Encrypt data at rest and in transit, and enforce role-based access controls so the right people on the right teams have the right access.
Govern the lifecycle. Define retention policies, ensure data quality, and maintain audit trails for every access and modification. Without governance, a data lake becomes a data swamp.
What are the benefits of a dedicated security data lake?
Improved threat detection. Analyzing all your security data together surfaces threats that individual systems would miss and reduces blind spots.
Faster incident response. With everything in one place, you can investigate incidents quickly and confirm blast radius without switching among many consoles.
Better threat hunting. You can search months or years of historical telemetry for indicators of compromise linked to newly discovered threats, including campaigns that went undetected when they occurred.
Stronger security posture. Understanding your security data better helps you make evidence-based protection decisions.
Lower costs. Offload expensive SIEM storage to low-cost object storage while retaining full-fidelity data, and route only what matters to premium analytics tools.
What are the real-world use cases?
Threat hunting. Query large amounts of past data, such as logs, traffic records, and event metadata, to identify traces of attacks that slipped past real-time defenses.
Detection and response. Correlate security events across diverse sources to reconstruct attack timelines and understand incident scope. Centralized data streamlines investigations for both real-time and post-incident analysis.
Security analytics and trend analysis. Use the lake as a long-term platform for trend analysis, threat pattern recognition, and continuous improvement of security operations.
SIEM augmentation. Extend your SIEM by offloading long-term retention to the security data lake. Your SIEM stays focused on real-time monitoring while the lake handles deep-dive investigations and historical correlation. This also accelerates SIEM migrations, since your data is not locked into one vendor's format.
What are the security and governance challenges?
A repository holding large amounts of sensitive security data is a prime target for attackers. Plan for these challenges up front.
Data access control. Granular, role-based permissions are essential but complex to manage across varied datasets.
Compliance and regulatory requirements. Data lakes often hold information governed by GDPR, HIPAA, and CCPA. Regulators increasingly expect long retention: PCI DSS requires at least one year of security log retention, HIPAA often requires six years, and SOX mandates seven years for relevant records. Ongoing compliance and audit trails are required.[citation needed]
Encryption and privacy. Protecting data in transit and at rest is crucial, and personally identifiable information (PII) requires careful handling. Masking sensitive data at ingestion is easier than remediating it later across petabytes of storage.
Lifecycle management. Retention, archiving, and deletion policies must scale with your data. Effective lifecycle management prevents data sprawl and keeps you compliant.
Scalability and performance. As volumes grow, balancing performance against security and governance requires continuous monitoring and optimization.
How do you build or evaluate a security data lake?
Start with the pipeline, not the storage bucket. Building a security data lake requires a platform that ingests large volumes of security data from SIEMs, firewalls, and cloud services, in real time or batches. Evaluate candidates for scalable and tiered storage, open formats with no proprietary lock-in, strong security and governance controls, support for standards like the Open Cybersecurity Schema Framework (OCSF), and the ability to search data in place without rehydration.
Separating compute from storage is the architectural shift that matters. It lets you retain large amounts of telemetry at low cost while analyzing it with the tools your team prefers.
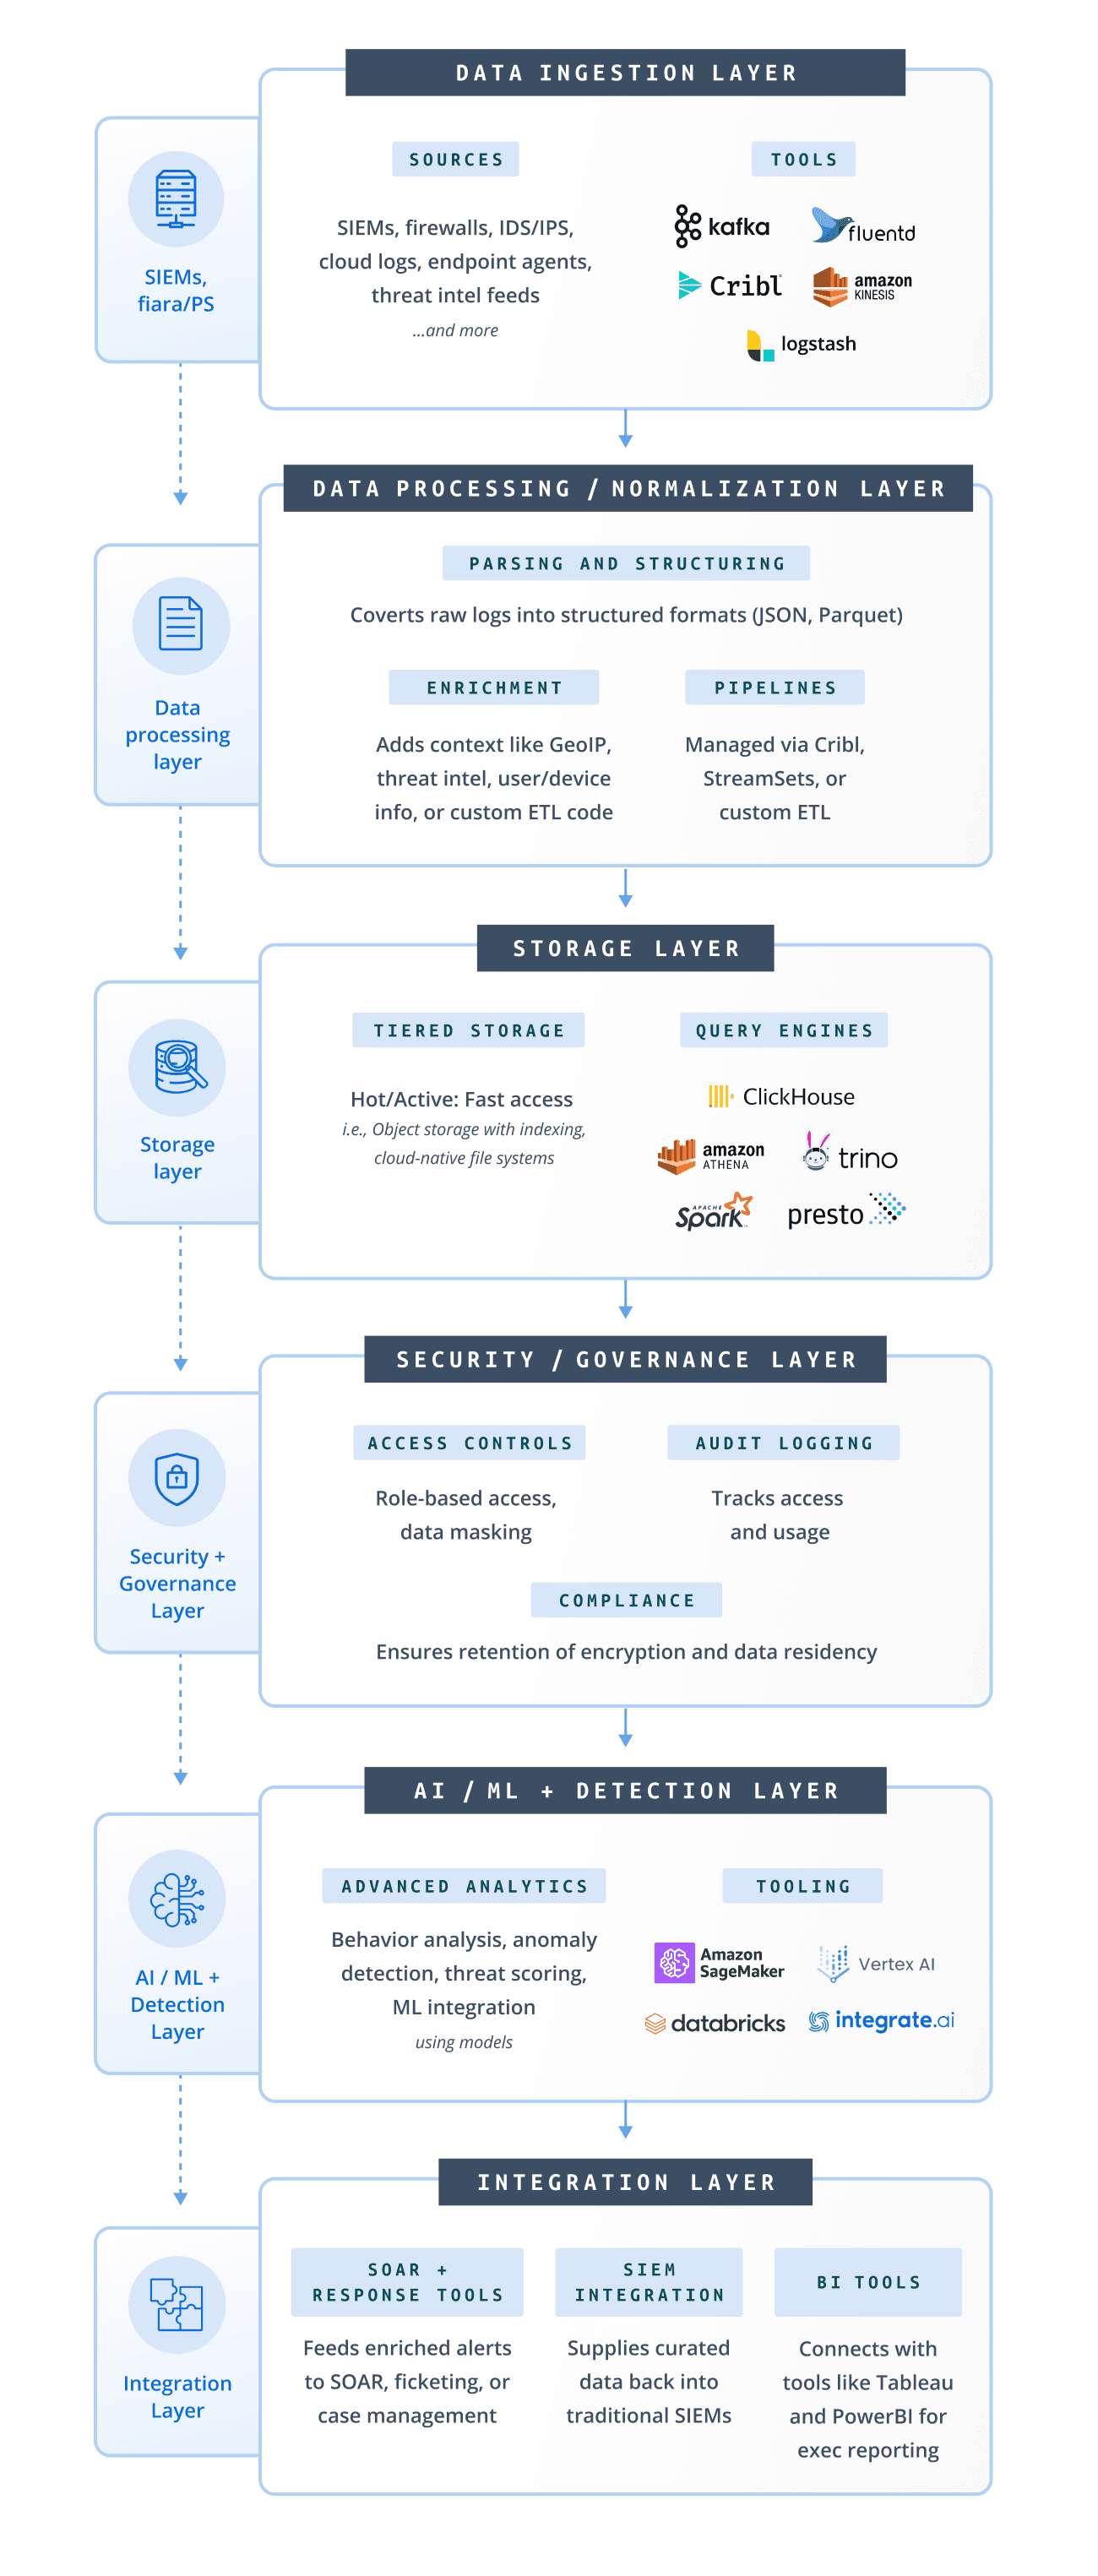
What's the future outlook for security data lakes?
Adoption is increasing for clear reasons. Rising SIEM costs and complexity push organizations toward schema-on-read architectures that store raw data first and apply structure only when needed. The demand for unified telemetry across cloud, endpoint, network, and identity sources makes a centralized repository important for visibility.
AI affects this trend. Agentic security systems query and correlate data at a scale humans cannot, and they need broad, governed access to complete telemetry. A security data lake built on open formats feeds both human analysts and automated systems. Standards like OCSF and services like AWS Security Lake promote interoperability and reduce data silos.
As these technologies mature, security data lakes are increasingly used in modern security operations for threat detection, investigation, and response.
How Cribl can help with your security data lake
Cribl provides tools for telemetry that aim to give IT and security teams choice, control, and flexibility to build a security data lake without cloud or data engineering expertise. Cribl Lake is a turnkey, cost-effective storage solution for large volumes of full-fidelity security data. Zero-configuration provisioning creates a usable cloud data lake in minutes. Schema-on-need delivers data in the format you need when you need it, and unified security policies help keep data safe from unauthorized access.
Your data stays yours. Cribl Lake stores data in open formats with no vendor lock-in, and bring-your-own-storage support means you decide where data lives: your object storage or Cribl's. Cribl Search runs queries directly on data in Cribl Lake, other data lakes, object stores, search APIs, and analytics solutions like OpenSearch, with no data movement or rehydration required.
Built on Cribl's Data Engine for IT and security, the full suite works together: Cribl Stream and Edge collect, shape, and route telemetry from any source, sending detection-critical data to your SIEM and full-fidelity copies to the lake. That can reduce SIEM costs, increase retention, speed investigations, and help maintain compliance.
Try the Lake Sandbox today and get hands-on.
Security Data Lake FAQs
What’s the difference between a security data lake and a SIEM?
A SIEM is a security analytics platform that collects, normalizes, and analyzes log data—often with limited retention and high costs. A security data lake, on the other hand, stores raw, structured, and semi-structured data at scale, offering more flexibility for custom analysis and long-term retention.
What types of data can be stored in a security data lake?
Security data lakes can ingest and store logs, metrics, traces, network traffic, endpoint data, cloud telemetry, and threat intelligence feeds—essentially any machine data relevant to security operations.
Is a security data lake secure?
Yes—when implemented with strong controls. Security data lakes rely on encryption, role-based access control, data masking, and audit logging to protect sensitive data and meet compliance requirements.
How does a security data lake improve threat detection?
By storing large volumes of diverse data for longer periods, a security data lake enables deeper correlation, anomaly detection, and retrospective analysis—leading to faster detection of advanced threats and root cause investigation.