Security Information and Event Management (SIEM) is a cybersecurity platform that collects, analyzes, and correlates security data from across your environment, on-premises and in the cloud, to give you a real-time view of threats. It is the place where firewall logs, endpoint events, identity records, and cloud audit trails meet, get compared, and turn into something an analyst can act on.
SIEM plays a central role in detecting, investigating, and responding to security incidents. By correlating events across systems that would otherwise never talk to each other, it surfaces suspicious patterns early, speeds up response, and helps you prove compliance. A SIEM is only as sharp as the data you feed it. More on that below.
What does SIEM actually do?
SIEM gives your security and IT teams one centralized platform for monitoring and analyzing security data. Instead of hopping between consoles, analysts get correlated events, real-time alerts, and the historical context needed to tell a real incident from background noise.
SIEM began as a passive compliance tool for collecting and storing logs. Over time it evolved into an active defense system that monitors events as they happen, applies analytics, and flags threats before they escalate. That shift mirrors a broader change in security: from looking backward at what happened to catching what is happening now.
Under the hood, SIEM merges two disciplines. Security Information Management (SIM) collects, stores, and manages log data generated by hardware and software across your organization. It is the long-term memory. Security Event Management (SEM) handles real-time monitoring, event correlation, and alert notifications. It is the reflexes. Put SIM and SEM together and you get a system that can both remember everything and react instantly, which is exactly what you need when the threat environment refuses to sit still.
How does SIEM work? The 9 stages of threat detection and response
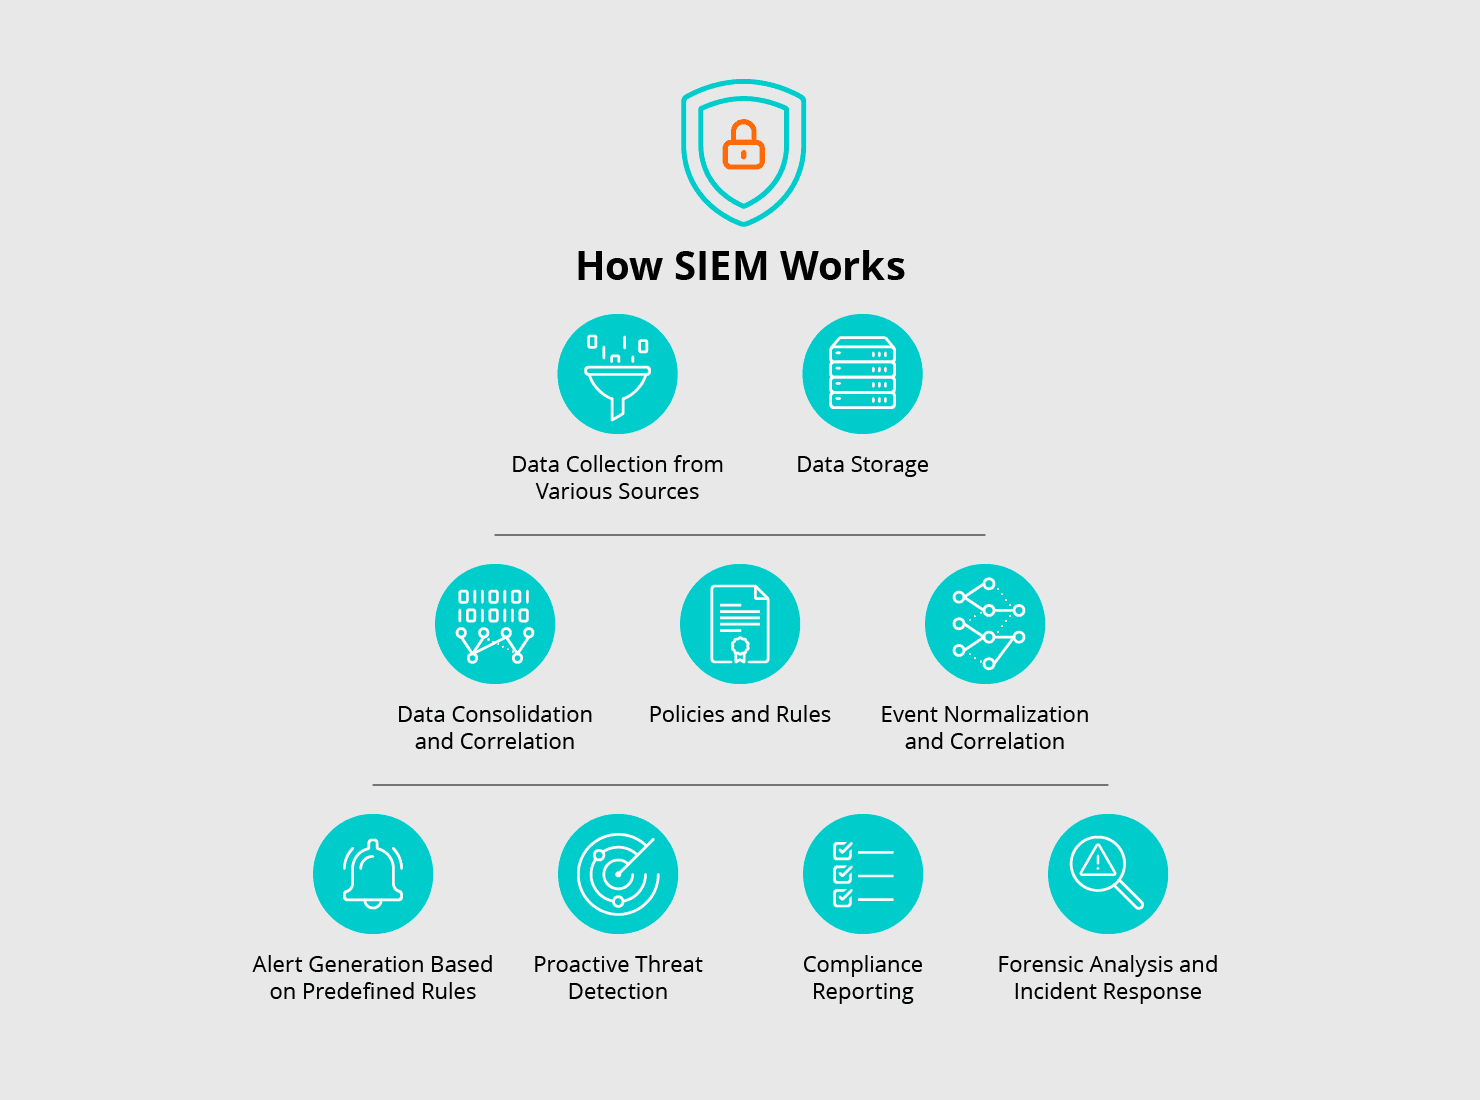
SIEM works by moving data through a repeatable sequence: collect, store, normalize, correlate, apply rules, alert, and investigate. Each stage builds on the one before it, and the whole cycle adapts to remote, hybrid, and in-office environments alike. Here is how it plays out in practice.
Data collection from multiple sources. Everything starts with ingest. SIEM gathers data from firewalls, servers, routers, endpoints, cloud services, and identity systems so you have visibility across the entire network, not just the parts that are easy to instrument.
Data storage. Collected data lands in a secure repository that supports both real-time monitoring and historical analysis. You can investigate what happened last quarter while keeping an eye on what is happening this minute.
Data consolidation and correlation. Raw logs in isolation are overwhelming. SIEM consolidates and correlates events from different sources, turning scattered data points into patterns you would not spot by looking at a single log file.
Policies and rules. Predefined rules describe what normal looks like and what does not. They weigh factors like IP address, device management status, and behavioral indicators so teams can spot potential threats quickly.
Event normalization. Normalization standardizes log entries into a common format. Once data is normalized, comparing a firewall event to an authentication event becomes straightforward, which makes anomalies easier to detect.
Alert generation. When normalized data trips a rule, SIEM fires an alert. Alerts prompt analysts to investigate and act.
Proactive threat detection. Modern SIEM platforms use machine learning and behavioral analytics to catch threats that rules alone would miss. This is where threat detection moves from reactive to forward-looking.
Compliance reporting. SIEM generates the detailed reports that regulations such as GDPR and HIPAA demand. Capabilities like data masking protect sensitive fields so you stay compliant without exposing what you should not.
Forensic analysis and incident response. After a breach, SIEM lets you retrace the attacker's steps, understand how it happened, and gather the evidence needed to contain the threat and prevent a repeat.
What are the types of SIEM?
SIEM is not one-size-fits-all. It comes in three main deployment models, and the right one depends on how much control you need, how fast you need to scale, and how much in-house expertise you can commit. Think of it as choosing between a home library you maintain yourself, a public library where someone else handles upkeep, and a curated library service that recommends the next book.
Whichever model you choose, the data challenge is the same. Every SIEM charges you, in dollars or in performance, for what you send it. That is why effective SIEM strategies start with what flows in, not which vendor logo is on the dashboard.
What are the core SIEM capabilities?
SIEM capabilities span log management, event correlation, incident monitoring and response, threat identification, and compliance reporting. Together they provide advanced visibility, a stronger security posture, and faster incident handling.
Log management
Log management is the cornerstone of SIEM: collecting, storing, and analyzing log data from every corner of your organization. Without logs, there is nothing to correlate and nothing to alert on. As SIEM use grows, log volume and costs increase. That is why many teams now look to reduce log volume to lower infrastructure costs before data ever reaches the SIEM.
Event correlation
Event correlation links related records and identifies patterns across them. It turns a failed login here and a privilege escalation there into a single story worth investigating.
Incident monitoring and response
This is where SIEM earns its keep. It does more than flag problems; it gives analysts the context and workflow to resolve them. During an active incident, SIEM is the control center that guides the response team from chaos to closure.
Threat identification
Threat identification moves beyond data collection into proactive defense. Using analytics and machine learning, SIEM can surface potential threats before they become active attacks, buying your team the time that matters most.
Compliance reporting
Compliance reporting is sometimes treated as a byproduct, but it is a core feature. SIEM produces the detailed reports auditors expect, and it does so consistently. This is about maintaining a security standard that regulators recognize and your customers trust.
What are SIEM best practices?
SIEM best practices come down to defining clear goals, centralizing and optimizing the data you ingest, keeping detection content current, and investing in the people who run the platform. A regular SIEM optimization belongs on every security team's project list, because a SIEM that is never tuned quietly becomes a SIEM that is never trusted.
Define clear goals for your SIEM implementation. Before you change a config, decide what success means: compliance, real-time monitoring, incident response, or all three. A thoughtful SIEM implementation starts with objectives that guide both rollout and evaluation.
Centralize your data. Aggregate data from every source into a single view so correlation actually works. Treat it as a command center for security telemetry rather than a pile of disconnected feeds.
Optimize the data ingestion process. Make sure the SIEM receives accurate, timely, and relevant data. Filtering noise, deduplicating events, and enriching context up front improves every downstream analytic.
Regularly update SIEM rules and signatures. Threats change frequently. Your rules should too. Stale detection content is how sophisticated attacks bypass a well-funded SIEM.
Ensure proper data retention. Retention is a compliance requirement and a practical necessity. Historical data reveals long-term trends and gives forensic investigations something to work with. Keep full-fidelity copies in low-cost storage rather than paying SIEM rates for every byte.
Train staff on SIEM operations and threat response. A SIEM is only as effective as the people operating it. Invest in training so analysts can use the platform to its full potential and respond with confidence.
Conduct regular reviews and audits. Treat audits as health checks. They expose gaps, inefficiencies, and rules that fire constantly but never matter.
Integrate SIEM with other security tools. SIEM is part of a larger ecosystem. Connecting it to firewalls, EDR, intrusion detection, and SOAR platforms creates a fuller picture and faster response.
Automate workflows. Automation speeds up repetitive tasks and reduces human error. Every alert an analyst does not have to triage by hand is time returned to investigation.
The common thread here is data discipline. According to the SANS 2025 SOC Survey, 42% of SOCs dump all incoming data into a SIEM without a retrieval or management plan, which drives up both noise and cost. The teams that get the most from SIEM are the ones that decide, deliberately, what goes in and where everything else lives.
What does SIEM optimization look like in practice?
Consider Yale New Haven Health, one of the largest healthcare systems in the Northeast. A routine firewall software update bloated their Palo Alto logs with redundant fields, pushing daily SIEM ingest well past their Splunk license limit. Rather than accept a bigger bill or sacrifice visibility, the team put a telemetry pipeline in front of the SIEM.
By stripping redundant and null fields before ingest, they cut Palo Alto log volume by 40% and brought daily ingest back under their limit without losing a single field needed for detection. The same pipeline centralized collection from more than 30,000 endpoints, masked sensitive fields in Epic logs to simplify HIPAA audits, and later made it possible to redirect data to Microsoft Sentinel and Azure Data Explorer in about two weeks when licensing costs changed.
Controlling the data layer affects cost, compliance, and platform choice. This is the same principle behind Cribl Detect, which moves detection and investigation closer to where the data lives instead of waiting for everything to land in the SIEM first.
Rethinking what belongs in the SIEM, and what doesn't
Most SIEM problems come from data decisions made before ingestion: what gets ingested, what gets dropped, and what gets stored in an expensive hot tier it never needed to occupy. Solve the data problem, and the SIEM begins to perform as expected.
Cribl Stream filters, normalizes, and enriches telemetry before it reaches your SIEM, so you pay for signal instead of noise. Cribl Edge extends that control to distributed endpoints and infrastructure, collecting data at the source. Cribl Lake provides a cost-effective place to retain full-fidelity telemetry outside the SIEM's hot storage, so compliance and long-tail investigations do not compete with your ingest budget. Cribl Search lets analysts query across hot and cold data wherever it lives, without rehydrating or duplicating it first.
Cribl Detect builds on that foundation by bringing detection and investigation closer to the data itself, so threats can surface earlier, detection readiness becomes measurable, and investigations do not stall waiting for data to land in one place. Controlling the data layer affects detection timing, readiness, retention, and costs.
SIEM FAQs
What is a SIEM?
SIEM, or Security Information and Event Management, is a cybersecurity tool that aggregates and analyzes security-related data from various sources in real-time. Its primary function is to provide comprehensive visibility into an organization’s IT infrastructure, enabling the detection and response to potential security threats.
What is the difference between SIM and SEM?
Security Information Management (SIM) focuses on the collection, storage, and analysis of log data for compliance and reporting purposes. Security Event Management (SEM), on the other hand, is concerned with real-time monitoring, correlation, and alerting of security events. Together, they form the backbone of SIEM, combining long-term data analysis with immediate threat detection and response.
What are the 3 types of SIEM?
The three types of SIEM solutions include On-Premise SIEM, Cloud-Based SIEM and Hybrid SIEM.
What is Cribl Stream, and how does it work with SIEM?
Cribl Stream is an observability pipeline that allows organizations to collect, process, and route data from various sources. It helps optimize the data flow into SIEM systems by filtering, normalizing, enriching, and routing data, ensuring that SIEMs receive only the most relevant and actionable data. This improves the efficiency and effectiveness of SIEM operations.
How does Cribl Stream help reduce SIEM costs?
Cribl Stream reduces SIEM costs by filtering out unnecessary or redundant data before it reaches the SIEM, thus lowering the amount of data that needs to be processed and stored. It can also compress and route less critical data to cheaper storage solutions, minimizing expensive data ingestion and licensing costs.
Can Cribl Stream work with any SIEM platform?
Yes, Cribl Stream integrates seamlessly with all major SIEM platforms, including Splunk, CrowdStrike, IBM QRadar, Exabeam, and others. Whether your SIEM is on-premises or cloud-based, Cribl can be used to optimize data flow and processing.
What benefits does Cribl Stream offer in terms of data enrichment?
Cribl Stream can enrich raw data with additional context, such as geolocation, threat intelligence, or custom metadata, before it reaches the SIEM. This enrichment provides greater insights into security events, allowing SIEM systems to perform more detailed analysis and helping security teams respond more effectively to potential threats.
How does Cribl Stream improve SIEM scalability?
Cribl Stream helps SIEM systems scale by filtering and optimizing data streams, ensuring that only high-value data reaches the SIEM. This allows your SIEM to handle larger volumes of data efficiently as your organization grows, without becoming overwhelmed by irrelevant or redundant information.
Does Cribl Stream support real-time data processing for SIEM?
Yes, Cribl Stream processes data in real time, ensuring that your SIEM system receives up-to-date information. This is critical for real-time threat detection and response, as it enables security teams to identify and address security incidents as they happen.
How does Cribl Stream enhance compliance reporting in SIEM?
By optimizing and enriching data streams, Cribl Stream ensures that SIEMs receive accurate, relevant information needed for compliance reporting. It helps generate detailed reports that meet regulatory requirements such as GDPR, HIPAA, and others, while also enabling data masking to protect sensitive information.
What kind of data can Cribl Stream handle for SIEM?
Cribl Stream can ingest and process data from a wide variety of sources, including firewalls, servers, routers, cloud services, endpoint devices, and more. It supports structured, semi-structured, and unstructured data, making it a versatile tool for optimizing SIEM data flow.