One of my favorite parts of being on the product marketing team at Cribl is writing blogs no one will read getting to work with our speakers and preparing them for the big stage at CriblCon.
This summer was spent flushing out outlines, talk tracks, and hosting dry runs. It's surreal that CriblCon 26 is happening next week!!! 🎉 If you’re one of the lucky ones that will join us in Chicago, then you know the CriblCon agenda is packed with so many great sessions. But alas, you can’t be in two rooms at once. AI isn’t that advanced, yet.
So I’ve put together a curated path if you’re an analyst looking to level up and learn how to investigate faster, cut out complexity, and get more out of your tools, data, and yes, AI. These are the talks to put on your session scheduler 👇
If you want practical guidance about hunting threats with an AI investigator
I won’t share how many call for papers submissions I had to score, but I will say if I had to take that number in shots, I’d be dead. And after reading through so many, there was one that really stood out. I literally screamed “YESSSSSS!” when I saw it, then demanded I be the content development manager for it.
I also won’t say I play favorites with my speakers. But Alex and Nicole were my favs. Their talk has it all: drama, suspense, threat hunting, AI, and two badass women in security.
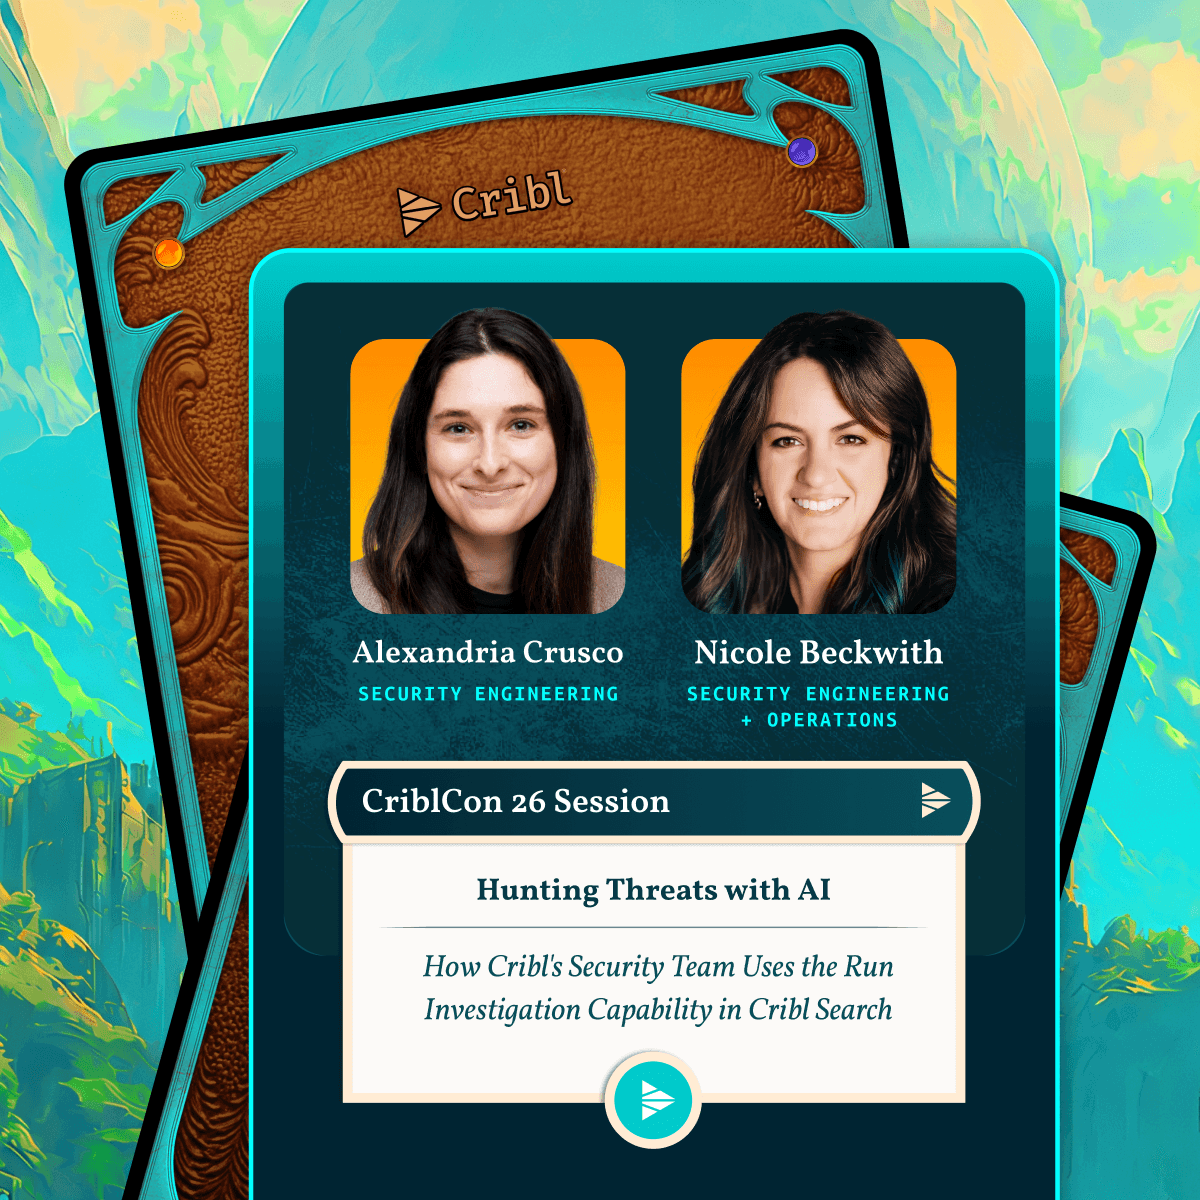
Hunting Threats with AI: How Cribl’s Security Team Uses the Run Investigation Capability in Cribl Search. Alex and Nicole are sharing how Cribl’s own security team uses AI-powered investigations to hunt threats, investigate anomalies, and respond across its environment—with real workflows, query and prompt strategies, and examples from the field.
The session will also address an important part of AI readiness: data quality. AI can only produce useful results when the underlying telemetry is complete, relevant, and enriched with the right context. If you’re interested in getting more practical about AI-assisted threat hunting, put this one on your list.
If you want to prepare future-you with a smarter storage and analysis strategy
This next one I know is going to be great because I built all the slides for it. Ok well, Gemini helped a bit too.
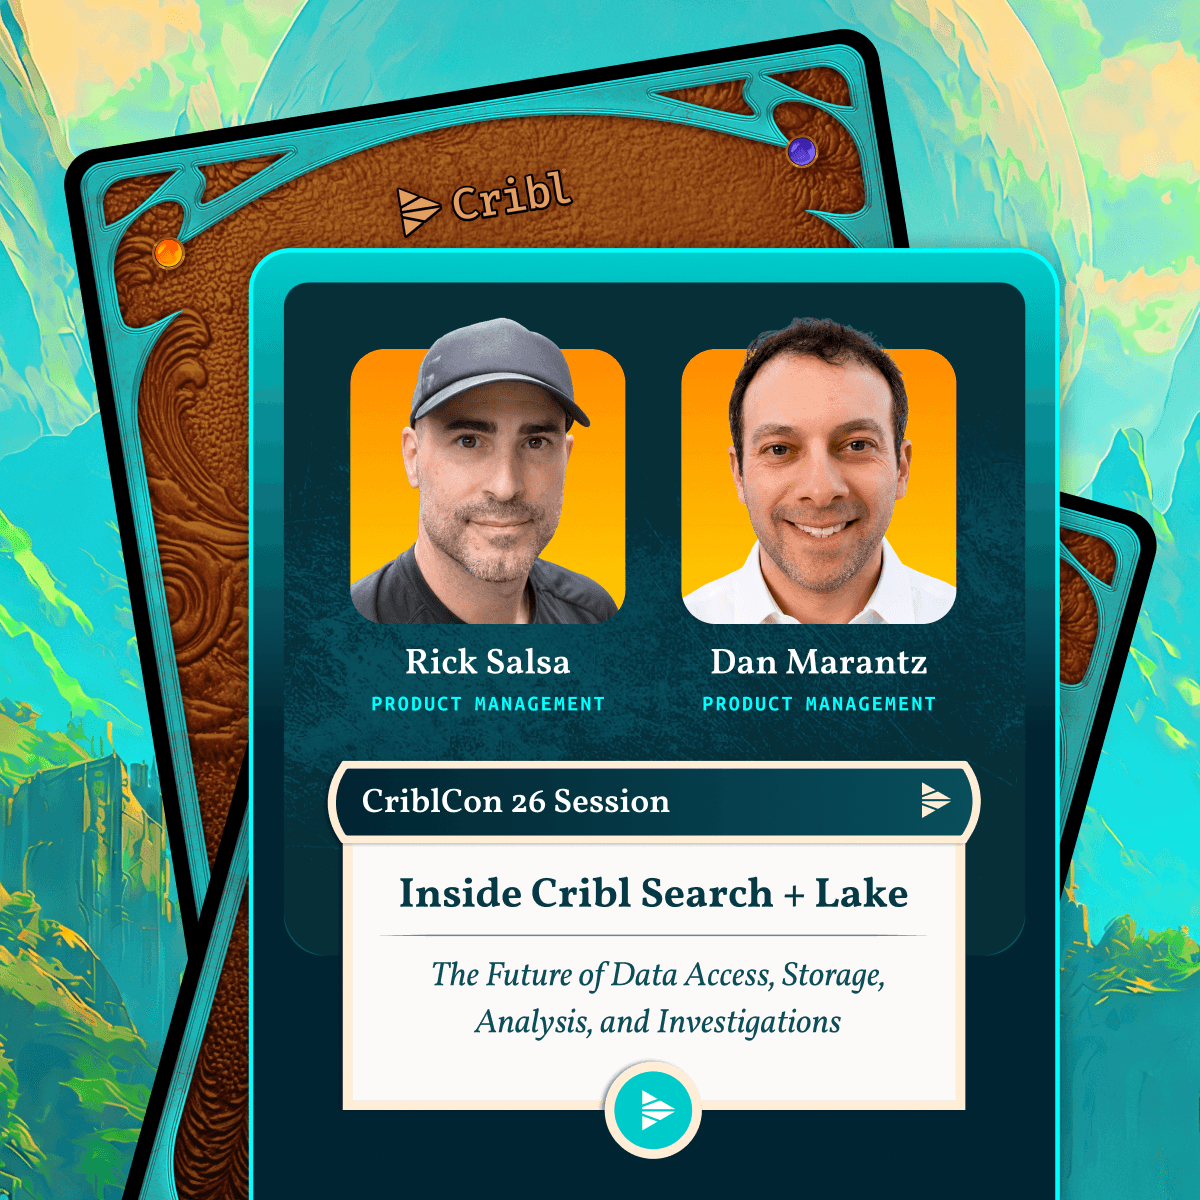
Inside Cribl Search and Lake: The Future of Data Access, Storage, Analysis, and Investigations. Dan and Rick are solving problems you’re all too familiar with: telemetry is growing rapidly, but access to historical and distributed data remains difficult. You’ll hear how Cribl Search’s federated and lakehouse engines, combined with Cribl Lake provide:
A unified search experience across environments
Cost-effective storage for high-volume telemetry
Access to data without unnecessary rehydration or movement
Faster, more flexible investigations
A path toward reducing SIEM dependency without sacrificing visibility
Spoiler alert: you should not have to choose between affordable storage and usable data. With the right architecture, you can store data where it makes sense and still access it when investigations demand it.
Next up: METRICSSSSSSSSSSSSSSSS!!
Can you hear my excitement around this one?
Metrics are exploding across AI workloads, Kubernetes environments, and modern applications. High cardinality is too damn high, and that growth creates new pressure to control costs.
David Cavuto and Roman Trusov (a truly dynamic PM/engineering duo) are getting on stage to share more about the new metrics capability built into Cribl Search’s lakehouse engine. Currently available in preview so you can be one of the firsts to check it out.
The session will teach you how to easily ingest, store, visualize, analyze, and alert on large volumes of metrics data while keeping it accessible for investigation. For platform engineers and observability leaders, this session connects metrics strategy to the broader Search and Lake story: bring more telemetry into a flexible architecture, make it easier to find, and move from signal to root cause faster.
If you want to learn which AI models are best for your investigations, workflows, and budget
This next one we weren’t even sure if it was even going to happen. Was the research extensive enough to present on? Would our attendees even care? We ultimately landed on yes and hell yea!
In June, I got summoned to HQ for a week to sit in on the conception of what is now called SecIT-bench, Cribl’s benchmark for evaluating AI across real-world security and IT scenarios. I still have no idea why I got to sit in the room because I had no technical expertise to contribute. I was there for moral support and smiles. But it was genuinely one of the coolest experiences ever: watching all the smart minds talk through which AI models to test, which real-world scenarios to throw at them, and how to build a benchmark that actually means something valuable.
Now, Sasi and Connor are sharing the results in their talk AI Showdown: Benchmarking Models for IT and Security Investigations. Come see what the models actually found and get some guidance in choosing the right AI models based on your workflows, priorities, and budget.
If you want to hear from Cribl customers directly
You don’t want to only hear from folks on Cribl’s payroll. Your peers are way more trustworthy. I get it. And honestly, we love nothing more than sharing customer stories. Cribl customers are true superstars: they’re the early adopters, trailblazers, and risk-takers pushing the industry forward. Their feedback directly shapes our product roadmap.
So if you want to hear how real organizations are using Cribl’s AI Platform for Telemetry in the real world in their real day-to-day jobs, there are two notable customer sessions to catch:
Prudential reduces root-cause analysis from hours to minutes
If your environment is complicated, your applications spread across cloud platforms and data centers, and your infrastructure segmented across networks, you can probably relate to the SRE team at Prudential. Cause when something went wrong, their support teams had to jump between multiple systems to piece together what happened.
Join Nick Coury and Emilio Garcia from Prudential: Enterprise Scale RCA with Cribl and AI: Reduce MTTR Agentically with Cribl Search. They’ll share how their team built a unified search strategy by bringing application and platform logs into a single search experience. From there, AI agents can investigate across cloud and on-prem environments without requiring humans to manually grant high-privilege access to every system.
Prudential’s approach connects agents directly to the data and context they need to investigate, troubleshoot, and get to the bottom of an issue. The result? Less time spent on manual triage, faster root-cause analysis, and better service-level outcomes.
Learn from SA Power’s live-fire incident response
Not only should you join this next one because the speaker is traveling all the way from Australia to present at CriblCon, but because he was also part of Cribl Search’s lakehouse engine limited availability program. Which means he’s been in the trenches with us, and has some good insider tips and tricks to share.
Incident response doesn’t wait around while you waste time hunting for the right data. Lindbergh Caldeira of South Australia Power Networks saw this firsthand during the organization’s Trident live-fire exercise. In Live-Fire Lessons: Accelerating Incident Response with Cribl Search Investigations and Notebooks, he’ll share what his team learned and how they streamlined investigations.
One big lesson? Investigate and document at the same time. Lindbergh will show how his team uses Search Investigations and Notebooks to search across data, build timelines, capture their work as they go, and spend less time piecing everything together after the fact.
Build your next investigation strategy at CriblCon
Together, these sessions tell a larger story.
Cribl Search and Cribl Lake provide the foundation for accessing and storing telemetry across environments. Cribl Metrics extends that foundation to the high-volume, high-cardinality data powering modern applications, Kubernetes, and AI workloads. Prudential demonstrates how the platform can support enterprise-scale, agentic root-cause analysis. South Australia Power Networks shows how Search Investigations and Notebooks can improve the incident-response workflow. Cribl’s security team brings the practitioner perspective on using AI effectively and responsibly. And our AI benchmarking session digs into which models actually perform best for investigations, workflows, and different budgets.
The common thread is control: control over where data lives, how it is accessed, how investigations are conducted, and how teams evolve their architecture over time.
Other worthy CriblCon sessions to check out
As the product marketer for Cribl’s Storage & Analysis line of business, I’m obviously a little biased about which sessions I want you to attend. Lucky for me, working with speakers is truly one of my favorite parts of my job, so I greedily volunteered to help with a few other sessions. Which means I can personally vouch that these are worth your time:
Apps on Cribl: Architecting for the Speed of Vibe Coding
Glenn Block and Nick Romito, aka the Godfathers of Apps, will dig into how platforms can help teams build applications at AI speed without sacrificing reliability. They’ll cover how trust boundaries, sandboxed execution, and managed backend primitives make it possible to build custom apps quickly, without putting your critical workflows at risk.
The Problem with Legacy SIEMs… And a New Path Forward
SIEM pain is nothing new: rising costs, exploding telemetry, and more complexity than anyone asked for. But what comes next? Bani, Jack, and Michael are going to talk about a new way to SIEM. They’ll unpack why the traditional collect → ingest → index → store model limits detection, retention, and investigation, and what happens when you put security outcomes and the data itself back at the center.
The Blueprint for Sustainable Scale: Operating Cribl as an Enterprise Platform
In this platform-focused session, Charles Hills and Alex Parella will show how teams can move from a single-team deployment to a secure, scalable enterprise platform. The session covers cost visibility, governance, access management, and the operational foundation needed to grow with confidence.
Explore the full CriblCon agenda for more details on each session, including the full abstracts, speaker bios, day, time, location. And honestly, you can’t go wrong with any session. And you definitely don’t have to listen to me (most people don’t!)
Can’t make it to Chicago? Don’t fret. Keynote and session recordings will be available after the conference on the CriblCon website. Stay tuned!