Why is SIEM tuning essential for your SIEM optimization strategy?
SIEM tuning is essential because an untuned SIEM buries real threats under alerts nobody has time to read. Managing a SIEM comes with its own headaches, from overwhelming alert volumes to making sure every notification is relevant and actionable. According to the SANS SOC Survey, 2025, 42% of SOCs dump all incoming data into their SIEM with no retrieval or management plan, which drives up both noise and cost.
Below are the three most common data management challenges and how to fix them.
How do you tackle alert overload?
Tackle alert overload by refining alert criteria and using analytics to match patterns. SIEMs are hypersensitive by design, and that sensitivity produces a barrage of alerts, many of them false positives. It strains your team and risks the one alert that matters getting lost in the pile.
Start by setting more precise criteria for what triggers an alert. Then add machine learning or behavioral analytics to spot patterns and suppress repeat offenders. Finally, put rule and parameter reviews on a schedule. Threats evolve, your network changes, and a rule that made sense last quarter may be pure noise today.
How do you cut the noise in your alert system?
Cut noise by adding context to alerts and using correlation rules that separate isolated events from actual attack patterns. Noise means irrelevant or non-critical alerts that clutter the console. Enough of it desensitizes analysts, and desensitized analysts miss real incidents.
Feed your alerting logic contextual information such as user roles, network segments, and asset criticality. A failed login on a test box and a failed login on a domain controller should not carry the same weight. Correlation rules that look for sequences of events, rather than single triggers, reduce the volume of alerts that deserve a human's attention.
How do you make sure alerts are significant and relevant?
An alert is only as useful as the action it prompts. If alerts aren't tied to your organization's specific security needs, they lead to wasted effort and overlooked vulnerabilities.
Review your SIEM settings and underlying threat intelligence regularly. Align operations with your actual risk profile and security policies, not a vendor default. And listen to the analysts on the ground. Their feedback is the fastest path to an alerting process that's both responsive and precise.
Tackling these challenges takes a mix of technical refinement and strategic management. Get both right and your SIEM stays an effective tool instead of an expensive log bucket.
How do you optimize your SIEM?
Optimize your SIEM by fine-tuning its rules, thresholds, and data quality to match your specific security needs, then test and audit it on a schedule. Every step below improves threat detection and response without adding a single new tool to your stack.
Tune your detection rules
Detection rules are the heart of your SIEM. Review them regularly so they reflect current threats and your organization's actual concerns. Remove outdated rules, adjust those that misfire, and add new ones for emerging threats. Rule hygiene is unglamorous, but it's the biggest lever in SIEM optimization.
Adjust your alert thresholds
Thresholds decide what counts as a potential incident. Set them too low and you're buried in alerts. Set them too high and you miss the critical ones. The right balance between sensitivity and specificity comes from periodic adjustments based on current threat intelligence and your own incident history, not from guesswork.
Normalize data before it hits your SIEM
Every source of security data tends to arrive in its own format. If you have a dozen sources feeding your SIEM, one user might appear with completely different field names in each one.

Multiply that across every user, every field, and every event, and the extra noise adds up fast. That inconsistent data makes building security rules, correlation rules, alerts, and dashboards difficult. You end up with visibility gaps that make threats impossible to detect.
It gets worse. Events that don't meet formatting requirements may be dropped by the SIEM entirely. Variations in data can also look anomalous, triggering unnecessary alerts. It's easy to go from missing threats you can't see to losing them in a list of alerts that never get reviewed. Data normalization before ingest fixes both problems and frees analysts to triage actual security issues.
Add context to the data in your SIEM
Usernames, whatever the format, carry valuable context. IP addresses are a different story. Look at this simple log entry from a Cisco ASA. All you really know is that one address is private and the other is public.
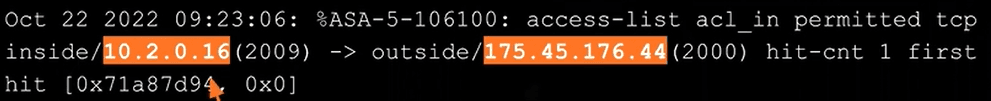
GeoIP information for those IPs is critical during an investigation, but jumping between tools to look up a location for every log burns valuable time. There's a subtler problem too. If you enrich at search time, you could attach today's GeoIP information to an IP address from a couple of years ago. In the example above, the external IP resolves to North Korea right now. A year from now it might not.
Enriching in the pipeline, at the moment the event is created, stamps the right context on the right event. Add network architecture, asset criticality, and user behavior patterns while you're at it. Analysts interpret alerts faster and overlook fewer critical ones.
Test your SIEM against real scenarios
Regular testing validates that your tuning actually works. Simulate security scenarios and watch how the system responds. Testing exposes detection gaps and points you to the next round of improvements, so the SIEM keeps up as threats evolve.
Monitor SIEM performance continuously
Track key indicators such as the number of alerts generated, response times, and the false positive rate. Continuous monitoring surfaces performance problems early, before they turn into missed detections or a blown license.
Audit your SIEM regularly
Audits review configurations, rules, and procedures. They catch outdated practices, compliance issues, and optimization opportunities that day-to-day monitoring misses. A regular audit cadence keeps your SIEM aligned with your organization's evolving security needs.
SIEM optimization is ongoing. Follow these steps on a cycle and you'll steadily improve your SIEM's efficiency and reliability. If you're standing up a new platform, our SIEM implementation guide walks through how to include these practices from day one.
How do you strike the right balance between data quantity and quality?
Balance collection by keeping everything you need for security, then deciding where each piece of data should live based on its value. Data volume is a problem in most environments. You are likely among organizations that do not ingest all the data they need into their SIEM. If infrastructure, network traffic, license costs, or agent load force you to skip sources, you likely have real security blind spots.
The most voluminous sources, like network flow logs, are often the most valuable from a security perspective. You should also collect DNS traffic and endpoint logs. But you need to do it in a way that lets you afford to run all the services you depend on. The more unnecessary data you collect, the further you drift from real-time alerting.
Cribl Stream helps existing tools handle rising data volumes while improving security. It normalizes, enriches, and reduces data. Stream lets you use data lakes for deep analytics, reporting, and searching without causing resource contention with your SIEM. Store a smaller, intentional portion of data in the SIEM, keep full-fidelity copies in object storage, and use Replay to push a session back through your SIEM when an investigation requires it.
You likely have the right tools in place already. Feeding them the proper data improves your security.
Detection shouldn't live or die by what your SIEM can afford to hold
Every optimization in this article comes down to one idea: your SIEM performs according to the data you feed it. Security teams are also treating the SIEM as one of several places for detection, investigation, and retention, rather than the only place.
Cribl is a vendor-agnostic hub that gives you control over that data. Acting between your sources and your tools, Cribl's data engine reduces volume and complexity without adding agents or disrupting the systems you already run. Cribl Stream processes events in flight. It normalizes field names, enriches events with GeoIP and asset context, drops null and duplicate fields, and routes each stream to the destination where it delivers the most value. Your SIEM receives clean, detection-ready data, and your license no longer absorbs unnecessary data. Cribl Edge applies the same processing at the endpoint, so you can shape and reduce logs and metrics at the source before they cross the network.
For high-volume sources you cannot afford to lose, Cribl Lake provides tiered, low-cost storage for full-fidelity copies in open formats. When an investigation needs history, Cribl Search queries that data where it lives, across Lake, object stores, and your existing tools, with no rehydration project required. Replay a targeted slice back into the SIEM when you need it.
This same approach underpins Cribl Detect, which brings detection, investigation, and retention onto an open foundation that works alongside your SIEM rather than forcing every security data decision through it. The goal is not to replace what you've already built. The goal is to stop asking your SIEM to be the detector, the archive, and the investigation tool all at once, and to give your team a more economical way to find threats earlier and understand where coverage is solid. The same pipeline also supports two-way data movement for migrations; our post on why SIEM migrations fail and how to break the cycle explains how
SIEM Optimization FAQs
What is SIEM optimization?
SIEM optimization is the ongoing process of tuning your SIEM's detection rules, alert thresholds, and data inputs so it detects real threats faster with fewer false positives. It covers rule hygiene, threshold adjustments, and normalizing and enriching the data you feed the platform. When configured correctly, it increases the usefulness of the tools you already own and can reduce the need to buy additional ones.
Why does my SIEM generate so many false positives?
False positives usually come from two places, alert thresholds set too low and inconsistent data formats that look anomalous to the SIEM. When multiple sources use different field names for the same user, correlation rules misfire and events that don't meet formatting requirements get dropped or flagged. Normalizing data before ingestion and tuning thresholds against real incident history are effective fixes.
Should I enrich data in my SIEM or in the pipeline?
Enrich in the pipeline. Adding context like GeoIP, asset criticality, or user role before data reaches your SIEM means events arrive ready for investigation, and analysts don't waste time switching between tools. Pipeline enrichment also records the context at the time of the event, so you avoid attaching today's GeoIP information to an IP address from two years ago.
How can I collect high-volume sources like network flow and DNS logs without exceeding my SIEM license?
Route a full-fidelity copy to low-cost object storage or a data lake, and send only the security-relevant slice to your SIEM. A telemetry pipeline such as Cribl Stream handles the reduction, normalization, and routing in flight. If an investigation needs the raw data later, you can replay it through the SIEM on demand.
How often should I tune and audit my SIEM?
Treat it as a continuous cycle rather than a project. Review detection rules and thresholds whenever threat intelligence or your environment changes, monitor KPIs like alert volume and false positive rate weekly, and run a full configuration and compliance audit at least quarterly. Testing with simulated scenarios confirms the tuning works.