6 Steps to Implement a Cloud Security Observability Strategy
If you’re hoping to build a successful cloud strategy that involves both observability and security, here are the 6 key steps to building a cloud security observability strategy:
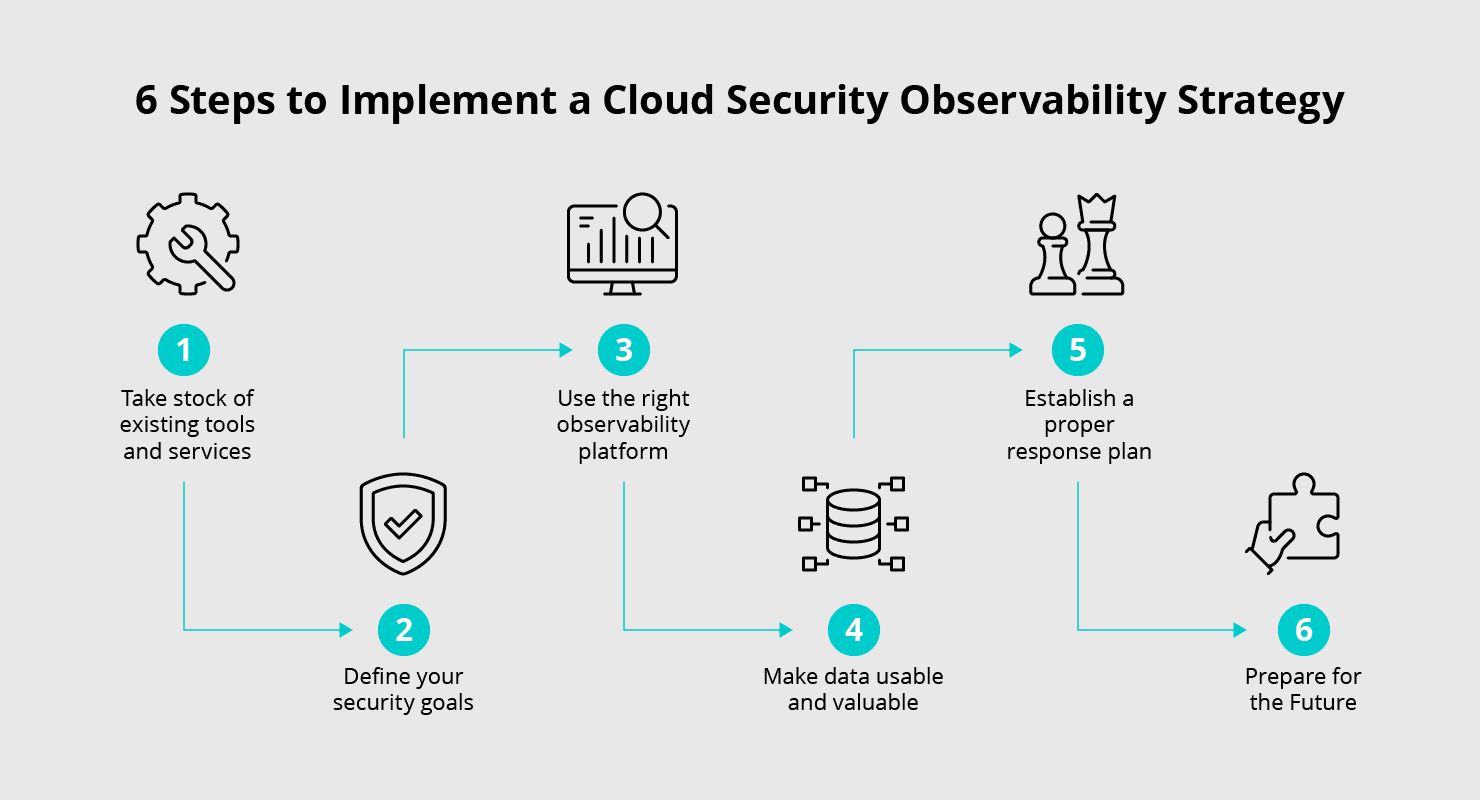
Take stock of existing tools and services
Start by identifying every system running in your cloud environment: the applications and services in production, the infrastructure keeping them up, and the tools moving and storing your data. This inventory defines the scope of your security posture and tells you exactly what needs protecting before you can protect it.
Define your security goals
Next, get specific about what you're trying to achieve. Do you need to detect threats in real time? Retain security data longer while cutting costs? Reduce the time between detection and resolution? Naming your goals up front lets you evaluate observability platform features against outcomes that matter, instead of chasing capabilities for their own sake.
Use the right observability platform
The right cloud observability platform helps you comply with regulatory and industry requirements while handling the large, elastic data volumes that cloud environments generate.
The right platform also improves collaboration across security, IT, and developer teams. When everyone draws from the same pool of observability and security data, teams move faster and stay aligned on what malicious activity looks like. A capable platform helps teams understand where and why performance issues occur, prevent unplanned downtime, and ultimately reduce overall cloud spend.
A vendor-agnostic data engine can help here. Cribl Stream is a control plane in front of your SIEM, data lakes, and analytics tools, giving security and IT teams a shared, consistent view of telemetry instead of fragmented silos.
Make data usable and valuable
A large volume of data is generated every minute, and most organizations struggle to make sense of it. Data that could have become valuable insight instead falls through the cracks and goes unused.
An effective security observability data pipeline collects, reduces, enriches, and routes data to the right destination. Moving data between regions, or between different public cloud platforms, adds another layer of complexity. A vendor-agnostic pipeline reshapes and transforms that data into a usable format so security teams can generate insights they can act on.
Cribl Stream and Cribl Edge handle this at the collection and routing layer, normalizing and enriching telemetry once so it arrives everywhere in a consistent, usable shape. For data that needs to be retained cost-effectively and queried later, Cribl Lake provides open, schema-on-need storage that keeps full-fidelity data accessible without the overhead of expensive hot storage.
Establish a proper response plan
Incidents require fast response. The longer it takes to resolve an issue, the more damage it can cause, and security teams need to act before sensitive data is exposed.
When data arrives from many sources in different formats, responding quickly becomes harder. A cloud observability solution helps you build a response plan before you need it.
First, the right people need to know their role and be held accountable. Observability notifies the relevant team members as soon as an issue surfaces. From there, responders need to pinpoint where the issue is occurring, understand why, and resolve it before end users notice an impact. After an incident is resolved, teams should run a root cause analysis and consider whether machine learning or automation could detect a similar issue faster next time.
Cribl Search helps analysts query data in place, across hot and cold storage, without waiting for rehydration. That means faster triage and less time spent moving data just to ask questions.
Prepare for the future
Data privacy and security requirements are becoming stricter. According to IBM's 2025 Cost of a Data Breach Report, organizations take an average of 241 days to identify and contain a breach, a number that should concern anyone relying on fragmented tools and manual processes. Protecting sensitive data will remain a high priority, and regulators are not getting more lenient.
A cloud security observability strategy, paired with cost-effective long-term retention in a platform like Cribl Lake, helps you adopt the cloud on time, under budget, and without risking your data's security. Fewer blind spots, fewer surprises, fewer 2 a.m. calls about breaches that went unnoticed.
Cloud security observability strategies help mitigate risk in cloud-native and cloud-first environments and give your organization more confidence to grow in the cloud while keeping data secure.
Your cloud strategy is only as strong as your telemetry foundation
Every step in this guide points back to one fact: you cannot secure what you cannot see, and you cannot see clearly when your telemetry is scattered across many disconnected tools. Cribl aims to close that gap. Cribl provides a telemetry platform, built on the Data Engine for IT and Security. It lets enterprise IT and security teams choose, control, and collect, shape, route, store, and search telemetry wherever it lives, without replacing the tools they already use.
Cribl Stream and Cribl Edge can collect and shape data across cloud, on-premises, and hybrid environments; Cribl Lake can retain full-fidelity telemetry economically for as long as compliance demands; and Cribl Search lets analysts investigate across all of it without moving data first. Together, these products turn a fragmented cloud security posture into one governed, searchable foundation.
Organizations that get ahead of cloud security risk treat telemetry as a strategic asset rather than an afterthought. If you're ready to build that foundation instead of adding another point tool, Cribl's team can help you map out what that looks like for your environment.
Implement a Cloud Security Observability Strategy FAQs
What is cloud security observability?
Cloud security observability is the practice of collecting and analyzing telemetry (logs, metrics, and traces) to get visibility into cloud environments so security teams can detect risk earlier, investigate faster, and demonstrate compliance. It extends traditional observability, which IT and developer teams have used for performance monitoring, into a proactive security discipline.
Why do organizations need a cloud security observability strategy instead of just observability tools?
Tools alone don't solve the problem. A strategy requires an inventory of existing assets, measurable security goals, and a response plan before an incident. Without that structure, teams have fragmented visibility, alert fatigue, and no clear path from detection to resolution.
How long does it typically take organizations to detect a cloud security breach?
According to IBM's Cost of a Data Breach Report, 2025, the global average time to identify and contain a breach is 241 days. Cloud environments, with many accounts, services, and regions, often widen that window without centralized telemetry visibility.
What role does a data pipeline play in a cloud security observability strategy?
A data pipeline collects, reduces, enriches, and routes telemetry to the right destination, whether a SIEM, a data lake, or an analytics tool. In multi-cloud environments, a vendor-agnostic pipeline like Cribl Stream makes that data usable rather than merely voluminous, so security teams can act on it.
How does Cribl help with cloud security observability specifically?
Cribl provides the data engine for a cloud security observability strategy. Cribl Stream collects, shapes, and routes telemetry across hybrid and multi-cloud environments. Cribl Edge extends collection to distributed sources. Cribl Lake provides cost-effective, full-fidelity retention for compliance and historical investigations. Cribl Search lets analysts query that data in place without waiting on rehydration.